


Automating Compliance Management for the Hybrid Enterprise
The Cavirin platform removes security compliance as a barrier to cloud (AWS, Azure, and GCP) adoption by automating compliance of the broadest set of frameworks (NIST, DISA, etc.), benchmarks (CIS OS, cloud, and Docker), and guidelines (SOC, ISO, GDPR, PCI, HIPAA) available today. A customizable policy framework provides flexibility for enterprises so you can craft your own combinations of benchmarks and set risk levels, enabling you to move critical compliance workloads to the cloud with confidence.
Challenges
- Implementing proper controls to achieve compliance.
- Access to documentation of compliance status for workloads running in the cloud and on-premise.
- Auditing and reporting across multiple clouds.
- Limited security controls being used by the cloud provider and the inability to know if they map to certifications required by your organization.
Compliance Requirements
- Automation of compliance through frameworks, benchmarks and guidelines.
- Ability to craft your own combination of benchmarks and set risk levels.
- Real time visibility into your vulnerabilities in a hybrid infrastructure.
- Simplified compliance reporting with prescriptive remediation.
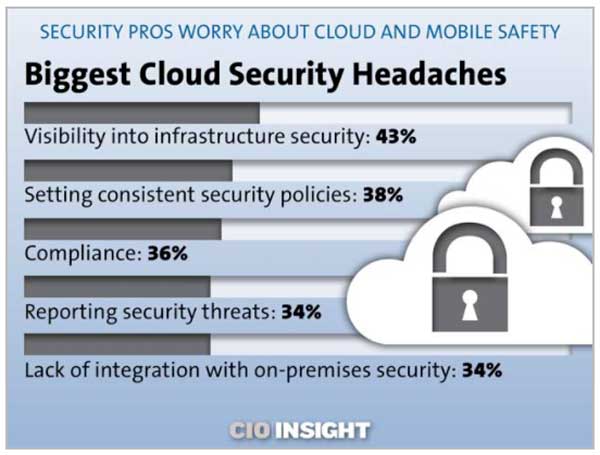

We group Cavirin’s adaptive security analytics capabilities into a grid, with predictive and preventative analytics; a potential game-changer for the CISO.
The Solution = Cavirin
- Regular assessments of security vulnerabilities with prescriptive remediations across your entire hybrid infrastructure (cloud, on-premise, and containers).
- Immediate reports/documentation to support compliance with internal security policies to expedite the auditing process.
- The richest library of security, risk, and regulatory frameworks with advanced compliance mapping. Co-author of both Docker and Kubernetes Security Benchmarks from the beginning.
- Complete visibility and management of your entire infrastructure enabling continuous improvement of your security posture.
- Intelligent, proactive, and preventative cybersecurity and risk management.
Benefits of Cavirin
- An automated robust cybersecurity, compliance and risk management based program utilizing the richest set of frameworks, benchmarks and guidelines available.
- A single pane of glass view for compliance automation of diverse, hybrid infrastructures (On-premise, cloud, and Docker/containers).
- Proactive security monitoring moving you from reactive to preventive. Improve results through data analytics and anomaly detection. Predict events and provide recommendations for auto remediation.
- Ability to fullfill multiple regulatory technical compliance requirements using advanced compliance mapping.
- Introduction of risk security and compliance into code during your development, staging, and deployment cycles.
Security Benchmarks and Compliance Regulations
Cavirin's complete set of fully automated technical controls (IT security frameworks, benchmarks, and guidelines) with remediation guidance is key to building and maintaining a security program when migrating to the cloud. Now you can prove compliance for regulatory audits in the cloud or any hybrid infrastructure.
Learn More
Learn More
Learn More
Learn More

Learn More

Understanding Your Role in the Shared Responsibility Model
The shared responsibility model is different for SaaS, PaaS, and IaaS, and within each, the choice of provider-based services vs those offered by 3rd parties can seem confusing. And, understanding what exactly the different layers of the model entail many times takes an equal analysis of the specific service in question. Given that organizations are adopting a multi and hybrid cloud approach, the IT team must take into account the different services and monitor interfaces across the different providers, and plan accordingly. Correlating data across multiple clouds, and introducing containers, yet adds another layer of complexity.
This eGuide provides you best practices for cloud account and workload visibility and security for the hybrid cloud, starting with but going beyond the shared responsibility model.